

Extended Security Lifecycle
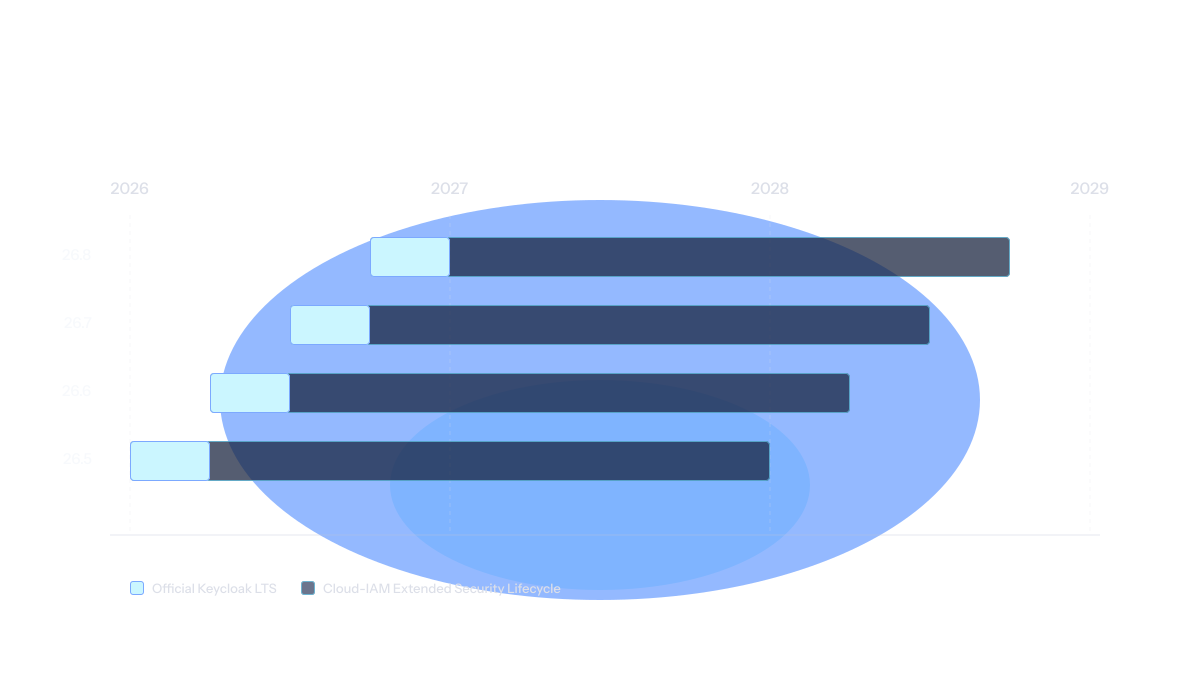
We backport security fixes to the exact Keycloak version you run up to three years after its release. Upgrade on your own schedule without staying exposed.

A critical CVE can be a nightmare. That's our job, not yours.
A new Keycloak version is released every three months, once it's out, the older versions stop receiving security patches. If you want to stay protected, you need to make a minor upgrade four times per year, and security patches up to every two weeks.
With the Extended Security Lifecycle, we extend security coverag for your Keycloak version beyond upstream EOL and patch it even when it is no longer the latest release.
Stay secure and update at your own pace.
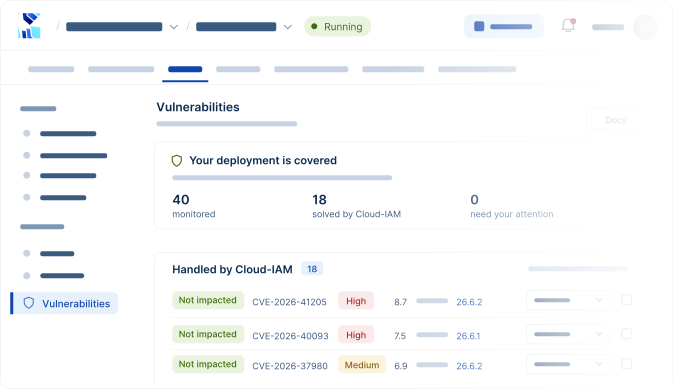
25+ CVEs
with a high or critical score in Keycloak so far in 2026
48h
average time to patch
1 to 3 years
of coverage
Plan your upgrades in advance and don't let CVEs dictate your priorities.
Pricing built around your setup.
Every deployment is different, so we price yours around what you actually need. Tell us about your project.

Everything you need
Our average time to assess, reproduce, test and fix CVEs is 48h.
Frequently Asked Questions
Can’t find your answer? Need any help?
Does Keycloak offer an LTS version?
Community Keycloak does not offer an LTS release. Only the latest community version is actively maintained, so older versions eventually reach end of life (EOL) and stop receiving upstream security patches. Cloud-IAM Extended Security Lifecycle bridges that gap by backporting fixes for qualifying critical and high-severity CVEs to the Keycloak version you already run.
Do I need to host with Cloud-IAM?
Today, yes. If you’d be interested in accessing patched Keycloak versions outside of Cloud-IAM, please contact us.
How is this different from my SLA?
The SLA guarantees uptime and support response. The Extended Security Lifecycle guarantees security fixes on a version you choose instead of just on the latest release.
What exactly counts as a covered CVE?
Critical and high CVEs (CVSS score of 7.0 or higher) affecting Keycloak core on your covered version. Performance issues and feature bugs follow the standard support path.